Sume webhook hostname with a private DNS answer is blocked entirely
If any A or AAAA answer for your Sume webhook_url hostname is private, the whole target is blocked. How the resolve-once check works and how to debug it.
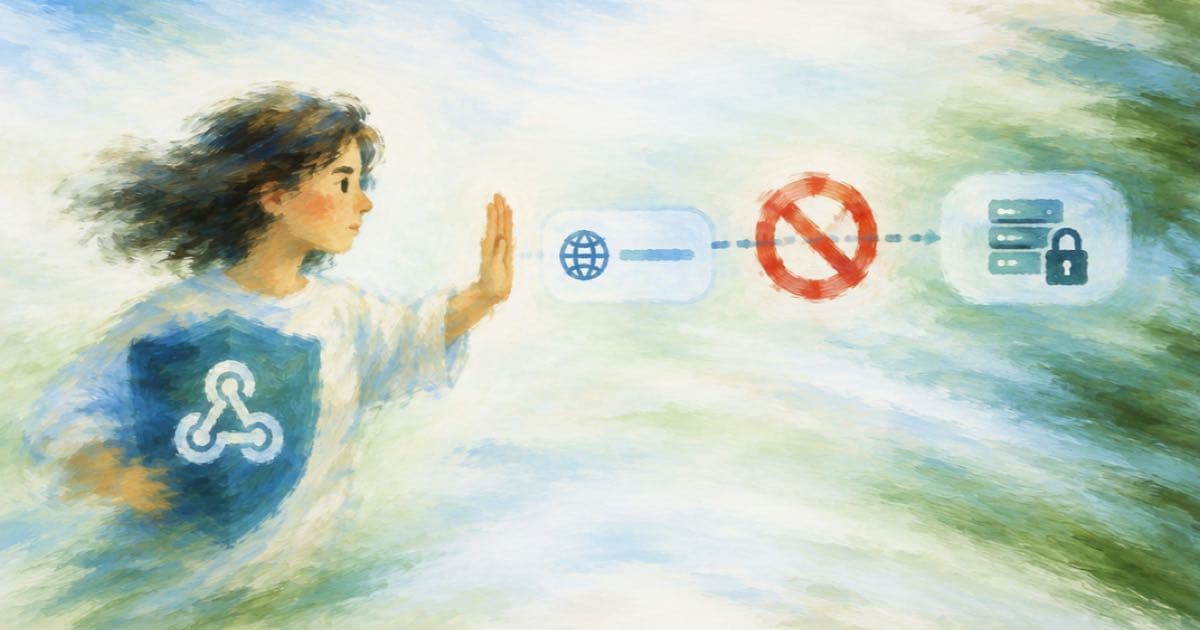
When Sume delivers a job webhook, it resolves your hostname once and blocks the target if any returned A or AAAA record is non-public. A hostname with one public and one private record is therefore blocked, not partly delivered.
This is a repo-level behavior in the delivery code. It protects against DNS setups that mix public and internal answers, and it is why a hostname that works from your laptop can fail from Sume.
How the check works
The worker looks up the hostname's addresses a single time and tests every answer. If all are public, it connects to those vetted addresses directly, so a second lookup cannot return something different. If even one is private, the target is blocked and the delivery fails without a retry.
| Answers | Outcome |
|---|---|
| One public address | Delivered to that address |
| Two public addresses | Connects to the vetted set |
| One public, one private | Blocked, failed, no retry |
| Only private (for example 10.x or 192.168.x) | Blocked, failed, no retry |
| No answer | Transient, retried |
Common causes
Split-horizon DNS, where an internal resolver adds a private record for the same name, is the usual one. Another is a wildcard or CNAME chain that ends on an internal load balancer. Record types matter too: an AAAA record pointing somewhere private counts just like an A record.
How to debug
Query both record types from outside your network and look for any non-public address.
The reason for a strict all-answers rule is that a DNS name with mixed answers can send different clients to different places. A check that only looked at the first answer could pass while the connection later landed on an internal address. Pinning the connection to the vetted set closes that gap, and testing every answer closes the mixed case. For you the consequence is simple: whatever a public resolver returns for the receiver hostname must be public addresses only, for both address families, every time you query it.
- Run dig A and dig AAAA for the hostname from a public resolver.
- Remove or fix the private record, or use a dedicated public hostname for the receiver.
- Then redeliver with POST /v1/jobs/{id}/webhook/redeliver.
Tradeoffs
The rule is strict and it will occasionally block a setup that is harmless. The alternative is a webhook that can be steered into your internal network, so a dedicated public hostname is a small price. If you cannot get one, poll.
Sources
Related posts
More in Developers
- What to log from a Sume MCP agent: ids and status, never signed URLs
Log request ids, job ids when needed, high-level status and sanitized media metadata. Keep API keys, signed URLs, raw private media URLs and transcripts out.
- Which AI video model makes a 25-second clip? Duration check in Python
Only some Sume video models accept 25 seconds in one request. See each model's duration range and filter a target length in a few lines of runnable Python.
- Which Sume audio endpoint do I need? TTS, STT, music, detach, split
Sume has separate endpoints for text to speech, speech to text, music, detaching video audio, and splitting or joining audio. Here is which to call for what.
- Which API: speech, transcript, music, captions or audio track?
Pick the Sume endpoint by the job: TTS for narration, STT for a transcript, Music for a score, captions for burned text, audio detach for a video's sound.
Written by Sume