Is mcp.dev.sume.com a staging URL I can use? No, use mcp.sume.com
mcp.dev.sume.com is for Sume's own development environments. Customer configs should use https://mcp.sume.com/mcp, and OAuth tokens are bound to that resource.
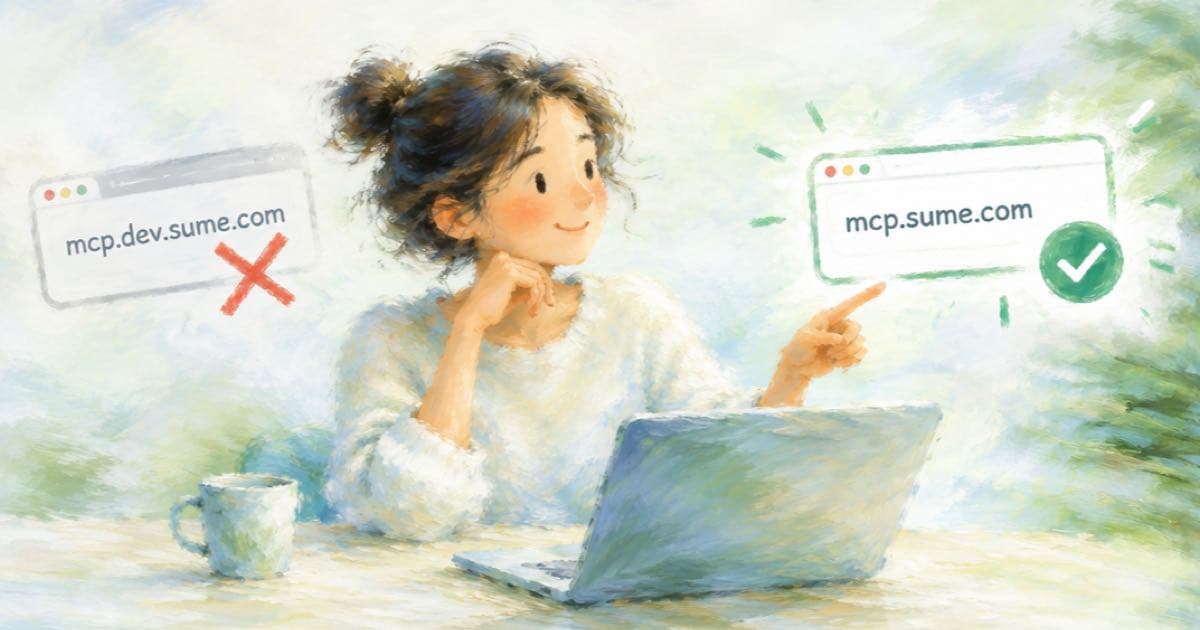
No. https://mcp.dev.sume.com/mcp is for Sume's own development environments. Sume's docs say public docs and customer configs must use https://mcp.sume.com/mcp. If your client config points at the dev host, fix it before you debug anything else.
The two hosts
The OAuth pages describe the same shape on both hosts: a protected-resource metadata document, an authorization server on the MCP origin, and dynamic client registration. The dev host just has a different origin.
| Host | Audience | Use it for |
|---|---|---|
| https://mcp.sume.com/mcp | Production | Cursor, Claude Code, Codex and other remote clients |
| https://mcp.dev.sume.com/mcp | Sume development | Sume's own testing, not customer configs |
Why a wrong host breaks quietly
An OAuth token is issued for one resource audience. Sume's token exchange checks that the client id, redirect URI and resource match the ones the authorization code was issued for, so a token or a code from one host is not a token for the other. A client that was registered or signed in against the wrong host can look connected and then fail on the first call.
An API key is a separate matter: do not paste a production key into a dev config just to see if it works.
- Some tools exist only on the dev host: Sume's tools page lists a dest-only group that is never available in production, so a tutorial that names one will not work against mcp.sume.com.
- Check the URL in your client config first, character by character.
- Run
mcp_healthafter connecting; it reports the endpoint, the auth source and the safety posture. - If a client cached metadata from the wrong host, remove the server and add it again.
What to do if you are already on the dev host
Remove the server entry, add https://mcp.sume.com/mcp, and sign in again so the client registers against the production authorization server. Do not carry over the old tokens, and do not copy a tool name from a dev-only note into a production prompt. Any jobs you started against another environment live there, not in your production workspace.
The tradeoff is small: a one-time reconnect. Staying on the wrong host risks confusing results about which environment holds your jobs and your balance.
Sources
Related posts
More in Integrations
- Meta Muse Zapier connector: how do I limit what an agent can spend?
Zapier's Muse connector brokers app access over Zapier MCP. Spend limits live in each tool you expose. Here is how Sume's scopes, caps and idempotency keys fit.
- provider.only on Sume image requests: why other slugs return 400
Porting an OpenRouter-style image call? On Sume, provider.only and order accept only sume; other slugs return 400 provider_not_available. Field rules.
- Render a Short over MCP: timeline_create, jobs_wait, timeline_get
Three hosted MCP tool calls turn a Timeline document into a vertical Short: create with an idempotency_key, wait on the job, then fetch the result.
- GitHub Actions job that renders a 9:16 clip on Sume as an artifact
A workflow file that replaces a Sora render step: submit to Sume, poll with a deadline, and upload the mp4 as a build artifact. The key stays in a secret.
Written by Sume